How to Evaluate a Background-Screening Proposal: A Procurement Scorecard
Published: 22 September 2026 | Last updated: 22 September 2026
Selecting a background-screening provider is not simply a price comparison. The provider may handle identity documents, employment histories, education records, criminal-record information, financial information and other sensitive personal data across multiple jurisdictions.Executive Summary
A defensible procurement process should answer three questions: can the provider lawfully and reliably deliver the checks required in every relevant country; can it protect candidate data and control its supply chain; and can it meet operational needs at the quoted price rather than simply present the lowest headline fee? This guide provides a practical 100-point scorecard for procurement, HR, compliance, security and legal teams evaluating background-screening proposals or running an RFP. The central principle: evaluate evidence, not assurances. Unsupported statements such as “global coverage”, “fast turnaround”, “compliant” or “secure” should not receive the same score as documented and independently verified capability.For related guidance, see eeCheck’s Background Screening Vendor Questions in Asia, In-House vs Outsourced Screening in Asia, Compliant Background Screening Policy in Asia and Background Screening Policy Template for Asia-Pacific.
Important: This framework supports procurement and risk assessment. It is not legal advice. Screening scope, consent, permitted sources, reportable information and retention requirements differ by jurisdiction and role.
1. Establish Pass / Fail Requirements Before Scoring
Some failures should not be offset by a low price or polished presentation. Set minimum requirements before reviewing commercial proposals.| Typical Procurement Gate | Why It Matters |
|---|---|
| Lawful delivery of every mandatory check in required jurisdictions | A broad country list is not useful if the required check cannot lawfully or reliably be delivered. |
| Acceptable DPA and cross-border transfer mechanism | Candidate information may move across entities, systems and jurisdictions. |
| Disclosure of material subcontractors and data sources | Buyers need visibility over who can access data and how delivery is controlled. |
| Minimum security controls | Encryption, MFA, access control, logging, vulnerability management and incident response should be evidenced. |
| Adequate insurance and financial stability | The provider should be able to support the programme throughout the contract term. |
| Breach-notification, audit, deletion and exit obligations accepted | These protections should be contractual. |
| No material misrepresentation | Misleading capability claims are themselves a procurement risk. |
| Legal, privacy, security and compliance review passed | High-risk issues should be resolved before award. |
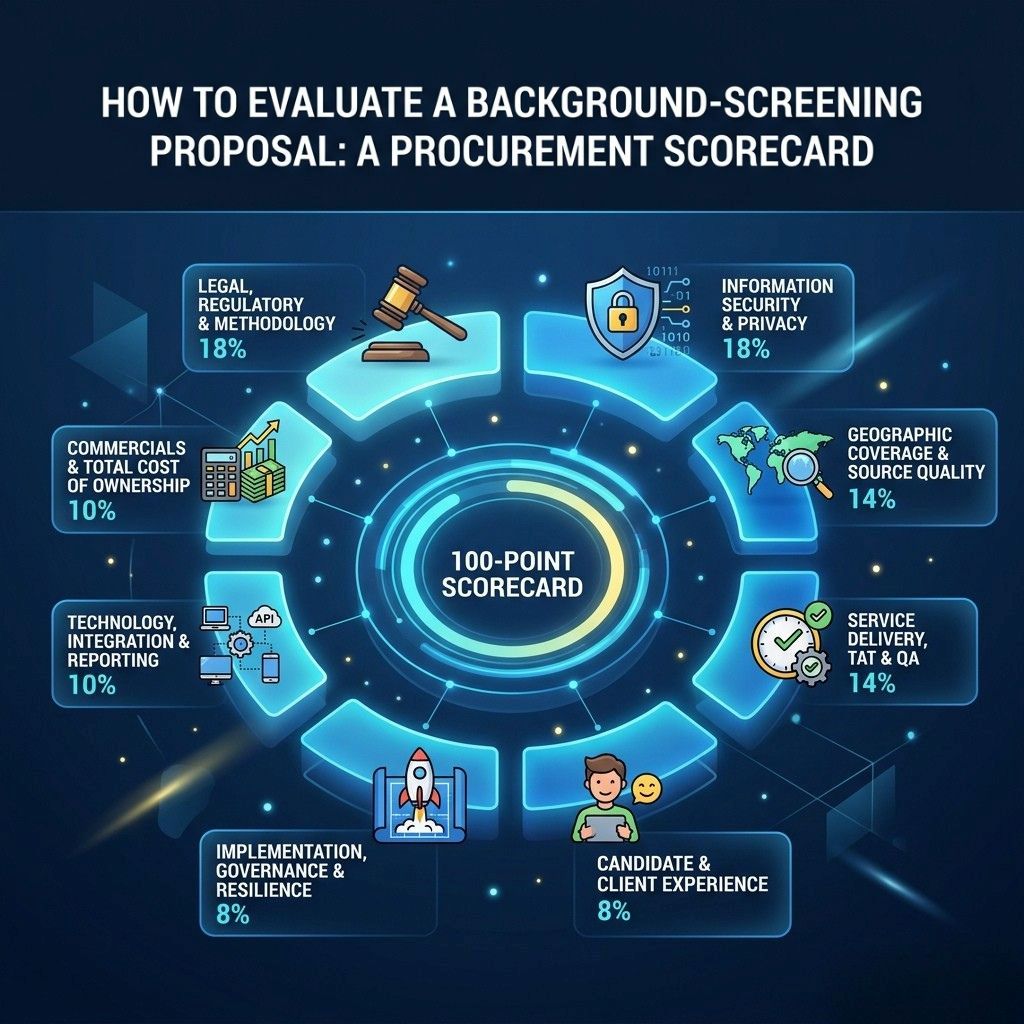
2. The 100-Point Procurement Scorecard
| Evaluation Category | Weight |
|---|---|
| Legal, regulatory and screening methodology | 18 |
| Geographic coverage and source quality | 14 |
| Information security, privacy and data governance | 18 |
| Service delivery, turnaround and quality assurance | 14 |
| Technology, integration and reporting | 10 |
| Candidate and client experience | 8 |
| Implementation, governance and resilience | 8 |
| Commercials and total cost of ownership | 10 |
| Total | 100 |
3. Use a Consistent Scoring Scale
Weighted score = (vendor score ÷ 5) × category weight| Score | Meaning | Evidence Standard |
|---|---|---|
| 0 | Unacceptable | Requirement not met, omitted or material risk identified |
| 1 | Major weakness | Largely manual, unproven or dependent on future development |
| 2 | Partially meets | Some capability exists, but important gaps remain |
| 3 | Meets requirement | Adequate capability supported by relevant documentation |
| 4 | Exceeds requirement | Strong, mature capability supported by performance evidence |
| 5 | Leading capability | Demonstrably superior, independently assured and contractually committed |
Scoring rule: score the provider’s current capability—not a roadmap item or a capability promised after contract signature.
4. Legal, Regulatory and Screening Methodology — 18 Points
What to assess
- Permissible screening scope by jurisdiction and role
- Consent or other required authorisation
- Identity and name-matching methodology
- Sources and verification routes
- Distinction between verified facts, source responses, database matches and observations
- Discrepancy, clarification and correction process
- Review of adverse findings
- Legal and regulatory change management
- Support for regulated-sector requirements
Evidence to request
- country-level methodology statements;
- sample redacted reports;
- consent workflows;
- reinvestigation procedures;
- regulatory change records;
- reporting rules; and
- source limitations and disclaimers.
Warning signs
- “Global criminal check” is presented as a single uniform product.
- The underlying source or verification route cannot be identified.
- Database searches are presented as equivalent to primary-source verification.
- The proposal guarantees that no record exists rather than describing the search actually performed.
- Compliance responsibility is pushed entirely onto the employer.
5. Geographic Coverage and Source Quality — 14 Points
Coverage should be evaluated at the country-and-check level, not by country count alone.What to assess
- Can the provider deliver every required check in each hiring country and candidate-history country?
- Is delivery performed through an owned team, affiliate, vetted local partner or aggregator?
- What source type is used for each check?
- Are source limitations, access restrictions and record coverage explained?
- Does the provider support local languages, scripts, name conventions and documentary requirements?
- Can it manage institutional fees, notarisation, translations and candidate-supplied documents?
- Are country-specific turnaround times based on actual performance?
- How are countries with decentralised or non-digitised records handled?
Evidence to request
Ask for a country-and-check coverage matrix containing, at minimum:| Coverage Matrix Field | Required Detail |
|---|---|
| Country | Jurisdiction in which the check is performed |
| Check type | Employment, education, criminal, credit, regulatory, identity, etc. |
| Verification route | Database, government source, institution, referee or local researcher |
| Source type | Primary, authoritative or secondary |
| Standard TAT | Median and 90th percentile, not just a broad range |
| Candidate action | Documents, consent, fingerprints, in-person visit or none |
| Additional fees | Institution, court, government, translation or access fees |
| Key limitation | Coverage period, geography, source availability or reportability |
| Delivery model | In-house, affiliate or subcontractor |
Warning signs
- Coverage is stated only as a country count.
- The provider will not disclose whether delivery is subcontracted.
- One turnaround promise is applied to all countries and check types.
- Reports omit the source searched, date searched or material limitations.
6. Information Security, Privacy and Data Governance — 18 Points
Security and privacy should carry at least as much weight as commercial terms.What to assess
- Current ISO/IEC 27001 certification or equivalent assurance
- Certification scope
- Encryption in transit and at rest
- MFA, least privilege and role-based access
- Logging, vulnerability scanning, penetration testing and patching
- Production/test separation
- Data storage and backup locations
- Cross-border and onward transfers
- Subprocessor access
- Retention and deletion
- Incident response and notification
- Applicable data-subject rights
- AI use and human oversight
Evidence to request
- certificates and scope;
- penetration-test summary;
- security architecture;
- subprocessor register;
- data-location schedule;
- incident response procedure;
- retention/deletion standard;
- BCP/DR test results; and
- cyber/privacy insurance.
Warning signs
- The provider relies solely on a cloud host’s certification.
- Certification scope does not cover screening operations.
- Subprocessors or data locations are undisclosed.
- Candidate data is retained indefinitely “for future use”.
- AI is described broadly without clear boundaries, validation or human review.
7. Service Delivery, Turnaround and Quality Assurance — 14 Points
What to assess
- Define when the TAT clock starts.
- Separate provider-controlled from source/candidate-controlled delays.
- Review median, 90th percentile and completion-within-SLA measures.
- Segment SLAs by country and check type.
- Review incomplete-information and non-response handling.
- Understand QA before report release.
- Review adverse-result escalation.
- Ask for error, rework, complaint and correction rates.
- Confirm named escalation roles and response times.
Evidence to request
- at least six to twelve months of comparable performance data;
- SLA definition and sample monthly service report;
- quality-assurance methodology and sampling rates;
- escalation matrix;
- staffing and capacity plan;
- business-continuity arrangements; and
- anonymised examples of delayed-case communication.
Warning signs
- Only “average TAT” is supplied.
- The SLA clock stops for broad or poorly defined exceptions.
- Extremely fast completion is promised despite reliance on slow primary sources.
- Quality is described as “100% accurate” without a methodology or correction process.
8. Technology, Integration and Reporting — 10 Points
What to assess
- Secure ordering and candidate data collection
- Status tracking, document exchange and reporting
- Role-based access, SSO, MFA and audit trails
- Package and approval configuration
- Production-ready ATS/HRIS/API integration
- API authentication, retries, errors and change management
- Consolidated and entity-level reporting
- Report and audit-record export
- Mobile, accessibility and multilingual support
Practical test
Require a scripted demonstration using realistic scenarios. Ask the provider to:- create a candidate in one jurisdiction;
- trigger a missing-information workflow;
- show a delayed source response;
- escalate a potential discrepancy;
- restrict report access by role;
- display the audit history; and
- export management information.
9. Candidate and Client Experience — 8 Points
What to assess
- Clear, mobile-friendly candidate journey
- Transparent explanation of why information is requested
- Country- and check-specific document requests
- Save-progress and reminder functionality
- Suitable support hours and channels
- Secure correction/challenge process
- Proactive client updates
- Measured complaint and escalation performance
Evidence to request
- candidate journey demonstration;
- supported-language list;
- support response and resolution statistics;
- candidate satisfaction results and methodology;
- complaint categories and trend data; and
- sample candidate communications.
10. Implementation, Governance and Resilience — 8 Points
What to assess
- Named implementation manager and credible work plan
- Clear responsibilities and acceptance criteria
- Pilot, UAT and controlled rollout
- Migration of packages, workflows, users and historical cases
- Training and change support
- Ongoing governance cadence
- Financial stability and capacity
- Continuity and recovery arrangements
- Exit plan covering data export, transition assistance and deletion
Evidence to request
- implementation plan and RACI;
- sample risk and issue log;
- governance and reporting calendar;
- continuity and disaster-recovery test summary;
- financial information or credit assessment appropriate to the contract;
- client references for comparable implementations; and
- exit-assistance schedule.
11. Commercials and Total Cost of Ownership — 10 Points
The cheapest unit price can become expensive when essential items are excluded.What to assess
| Commercial Area | What to Clarify |
|---|---|
| Package content | What is included in each check and package? |
| Fixed fees | Minimum commitments, platform, account and implementation fees |
| Third-party costs | Court, institution, government, translation, courier and cancellation fees |
| Exceptions | Unable-to-verify, duplicate, reopened and supplementary checks |
| Technology | Integration, configuration, training and reporting |
| Pricing basis | Country, currency, contract year and volume assumptions |
| Price changes | FX, inflation and pass-through increases |
| Exit | Transition and termination costs |
Warning signs
- Large parts of pricing are marked “at cost” without an estimate or cap.
- Low base prices exclude common source fees.
- The proposal assumes volumes or contract terms not stated in the RFP.
- Price-adjustment mechanisms are unclear or open-ended.
- Service credits are the sole remedy for serious security or compliance failures.
12. Ready-to-Use Evaluator Worksheet
| Category | Weight | Vendor Score (0–5) | Weighted Score | Evidence / Reference | Evaluator Comments |
|---|---|---|---|---|---|
| Legal, regulatory and methodology | 18 | ||||
| Geographic coverage and source quality | 14 | ||||
| Security, privacy and data governance | 18 | ||||
| Service delivery, TAT and quality | 14 | ||||
| Technology, integration and reporting | 10 | ||||
| Candidate and client experience | 8 | ||||
| Implementation, governance and resilience | 8 | ||||
| Commercials and total cost | 10 | ||||
| Total | 100 |
13. How to Run a Fair Evaluation
- Use a cross-functional panel. Include HR/TA, procurement, privacy/legal, information security, compliance, HR technology and representative business users.
- Separate technical and commercial evaluation. Assess capability and risk before price dominates the process.
- Moderate scores as a group. Discuss material differences and retain the final rationale.
- Validate high-risk claims. Use due diligence, references, scripted demonstrations and, where appropriate, a pilot.
- Convert winning claims into the contract. Material promises should become contractual or implementation obligations.
14. Suggested Decision Thresholds
| Result | Suggested Treatment |
|---|---|
| Any mandatory gate failed | Do not proceed unless the risk owner formally accepts a documented remediation plan before award |
| Below 60/100 | Material capability or control gaps; normally exclude |
| 60–69/100 | Potentially viable only with defined remediation and stronger contractual controls |
| 70–79/100 | Meets requirements; compare risks, references and total cost carefully |
| 80–89/100 | Strong proposal with good supporting evidence |
| 90–100/100 | Exceptional; validate that scoring is evidence-based and not inflated |
15. Common Procurement Mistakes
| Mistake | Better Approach |
|---|---|
| Giving price too much weight | Consider delays, rework, breaches and unreliable results as part of total value. |
| Treating all checks as commodities | Compare sources, permissions, limitations and TAT like-for-like. |
| Scoring policies without testing implementation | Use demonstrations, audit evidence and operating records. |
| Accepting global claims without country detail | Require country-specific methodology, source, TAT, candidate requirements and fees. |
| Ignoring the provider supply chain | Understand which institutions, databases, researchers and partners can access data. |
| Leaving exit planning until the end | Define data export, open-case transition, secure deletion and assistance before award. |
16. How eeCheck Can Support a Procurement Evaluation
eeCheck provides background-screening services across Asia and internationally, including employment and education verification, identity, criminal and court-related searches where legally available, sanctions and PEP screening, adverse media and other role-appropriate checks. For procurement exercises, eeCheck can provide country-level service information, implementation planning, security and quality documentation, sample reporting and a structured response aligned with the buyer’s evaluation framework. Organisations should assess eeCheck using the same evidence-based standards set out in this guide and select the provider that best fits their legal, risk, operational and candidate-experience requirements. Related reading: Asia Background Screening Intelligence Report, Asia Background Screening Executive Briefing, Top Background Check Firm in Asia and MNC Background Screening in Asia.Frequently Asked Questions
What is the most important principle when evaluating a background-screening proposal?
Evaluate evidence, not assurances. Unsupported claims should not receive the same score as capabilities backed by current documentation, independent assurance, service data, demonstrations or contractual commitments.
Should the lowest-price background-screening provider win?
Not necessarily. Price matters, but buyers should compare total cost of ownership, including third-party fees, integration, exception charges, internal workload, delays, rework and risk exposure.
How much weight should security and privacy receive?
This framework assigns 18 points to information security, privacy and data governance—equal to legal, regulatory and methodology considerations.
How should country coverage be evaluated?
At the country-and-check level, including source type, verification route, candidate requirements, TAT, fees, limitations and delivery model.
How should a provider’s turnaround time be assessed?
Review the SLA clock, exclusions, median and 90th-percentile performance, completion-within-SLA measures and country/check segmentation.
What score is generally acceptable?
The framework suggests 70–79 as meeting requirements, 80–89 as strong and 90–100 as exceptional, while mandatory gate failures should be addressed separately.
Why should proposal claims be written into the contract?
A proposal score has limited value if material commitments on scope, methodology, security, service levels, pricing, implementation, transition and deletion do not become contractual obligations.
Final Takeaway
The right provider is not necessarily the bidder with the longest country list, fastest headline turnaround or lowest unit price. A strong procurement decision identifies the provider that can demonstrate lawful methodology, reliable sources, effective data protection, measurable service delivery and a workable operating model.A documented scorecard makes the decision more consistent and defensible—and forces the buying team to define its true requirements before marketing claims and price pressure take over.
About This Guide
Author
eeCheck Research & Editorial Team
Reviewed by
Cora Chang, Manager, Internal Audit & Operational Assurance, eeCheck
Last reviewed
September 2026
Methodology: This guide draws on eeCheck’s operational experience supporting regional background-screening programmes and on common vendor-governance practices. Suggested weights and thresholds are illustrative and should be adapted to the organisation’s service scope, contractual commitments and risk appetite.
Limitations: This article provides general operational guidance and does not constitute legal, regulatory or procurement advice. Requirements vary by jurisdiction, sector, check type and organisation.

